Learn how to use Cortex XSOAR with BloodHound Enterprise to monitor and manage attack path findings.
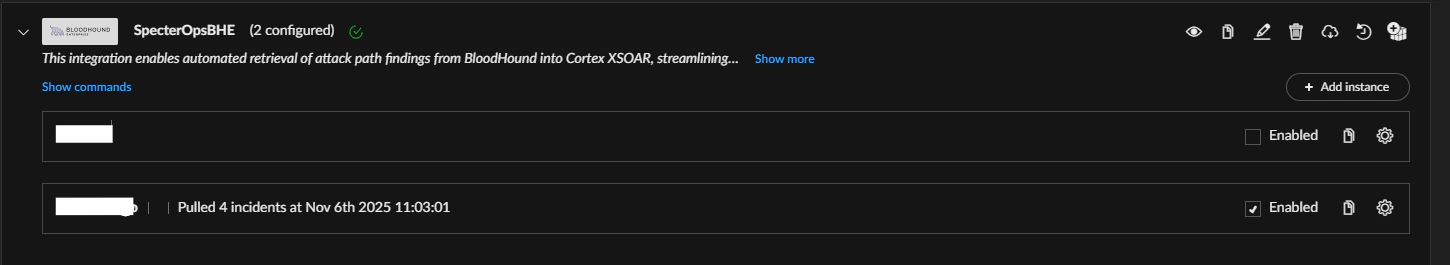
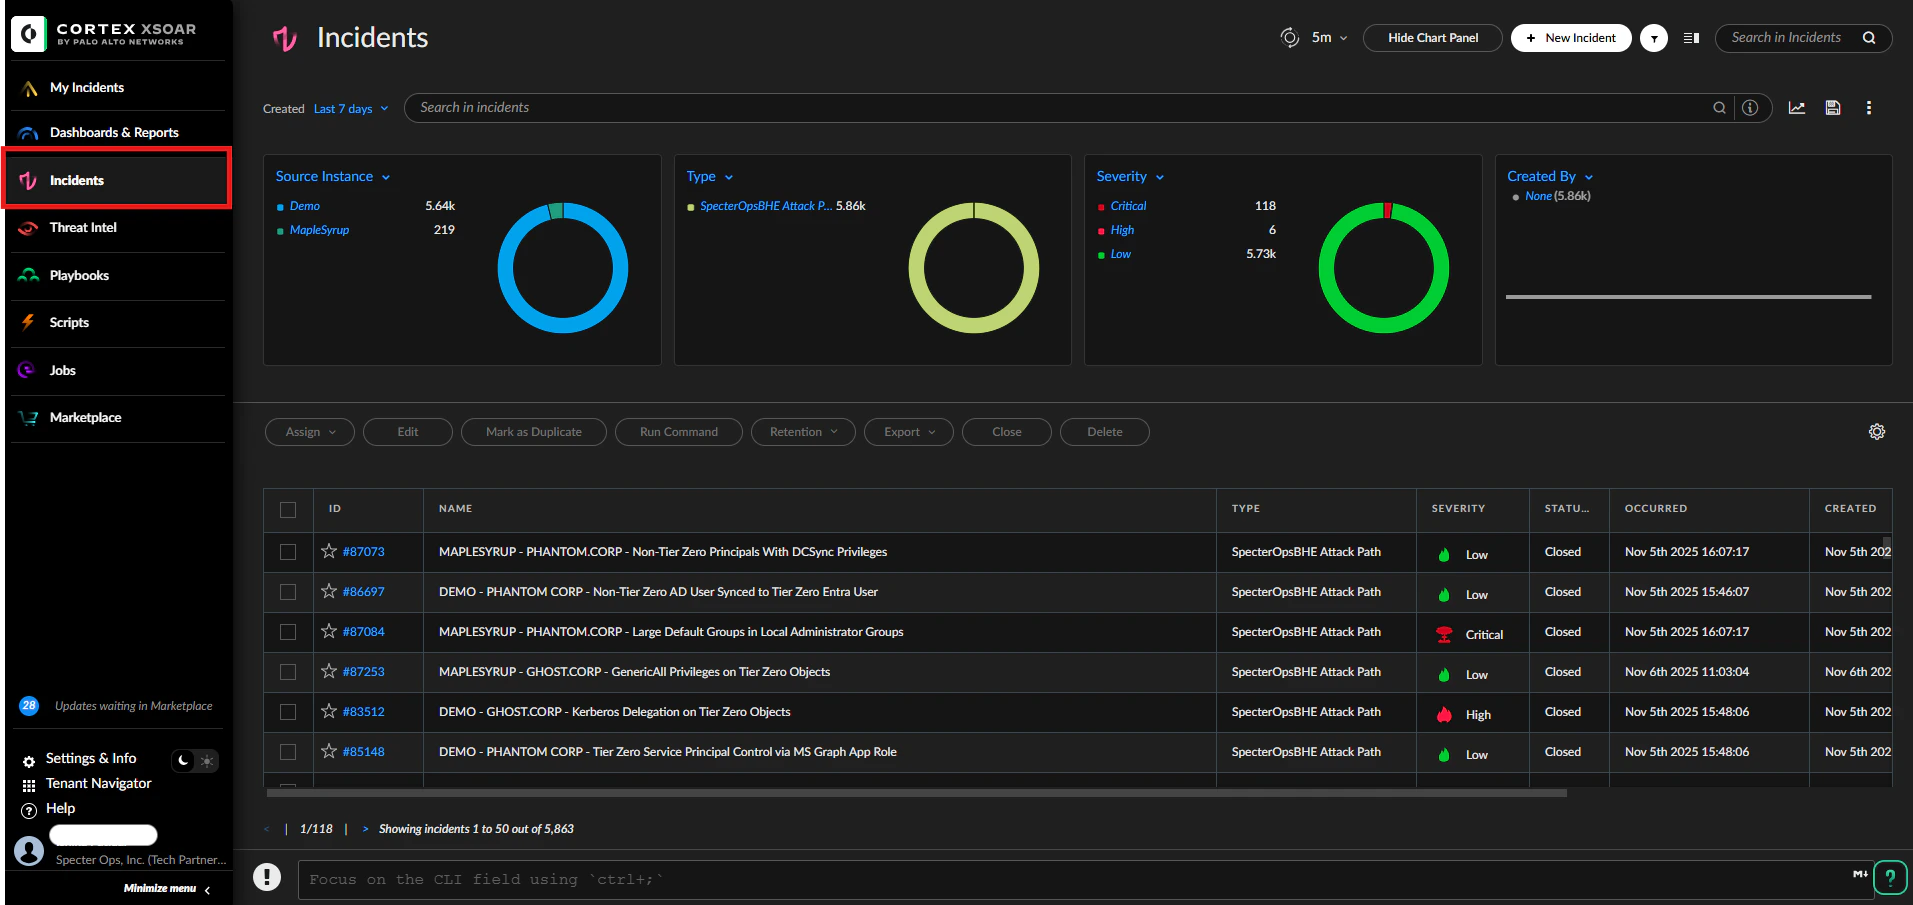
After you configure the integration, Cortex XSOAR begins fetching BloodHound Enterprise attack path findings as incidents. Use the sections below to monitor ingestion, view incidents, and inspect details.
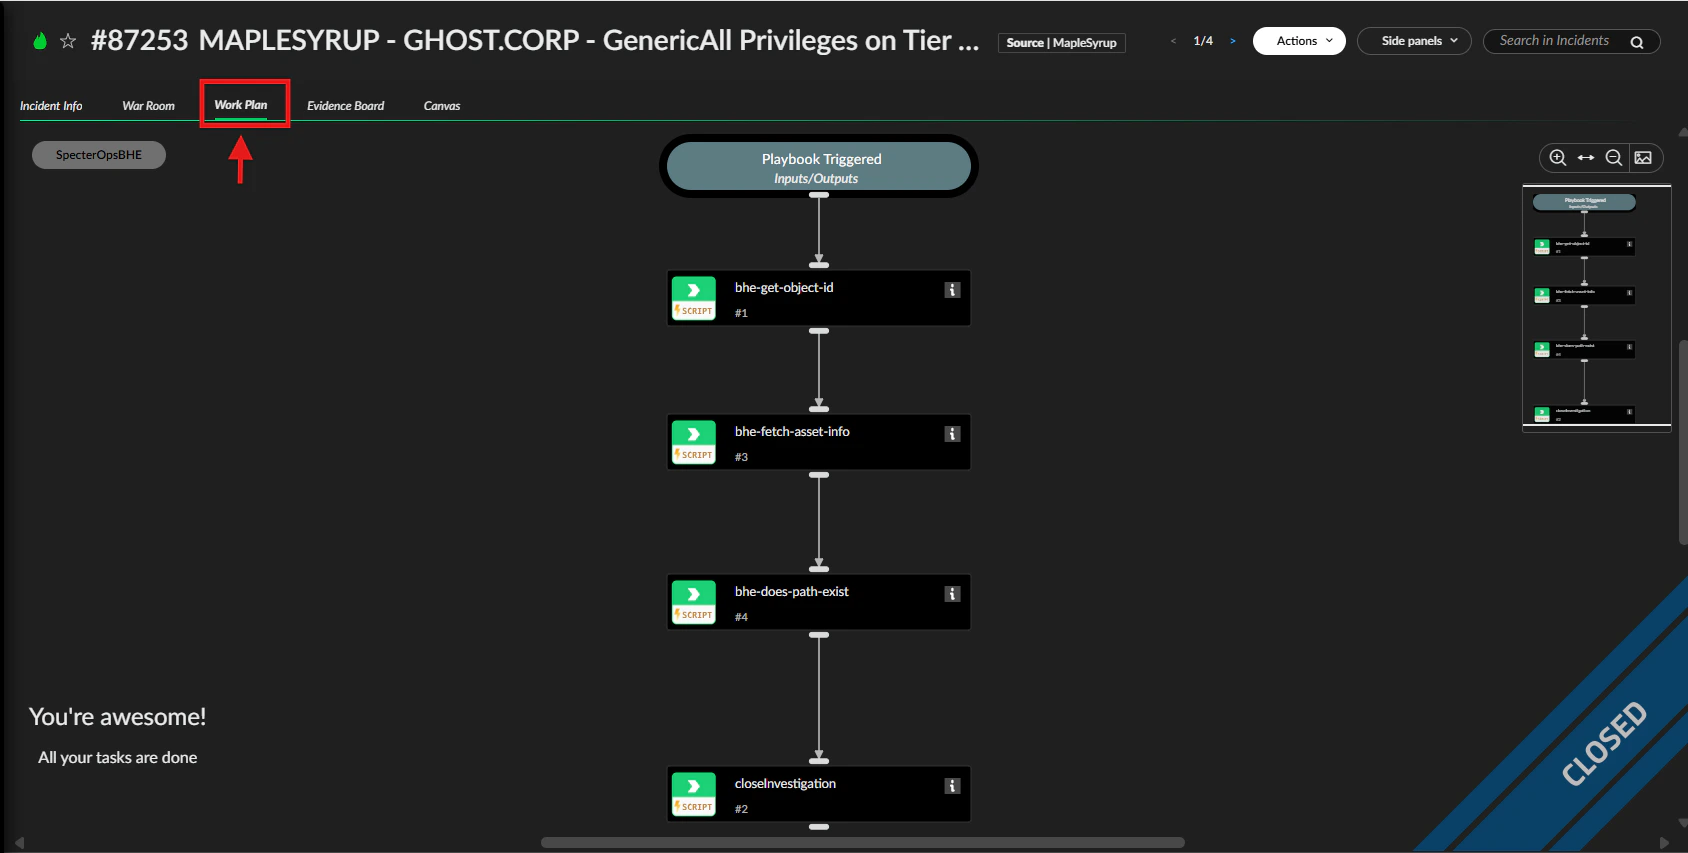
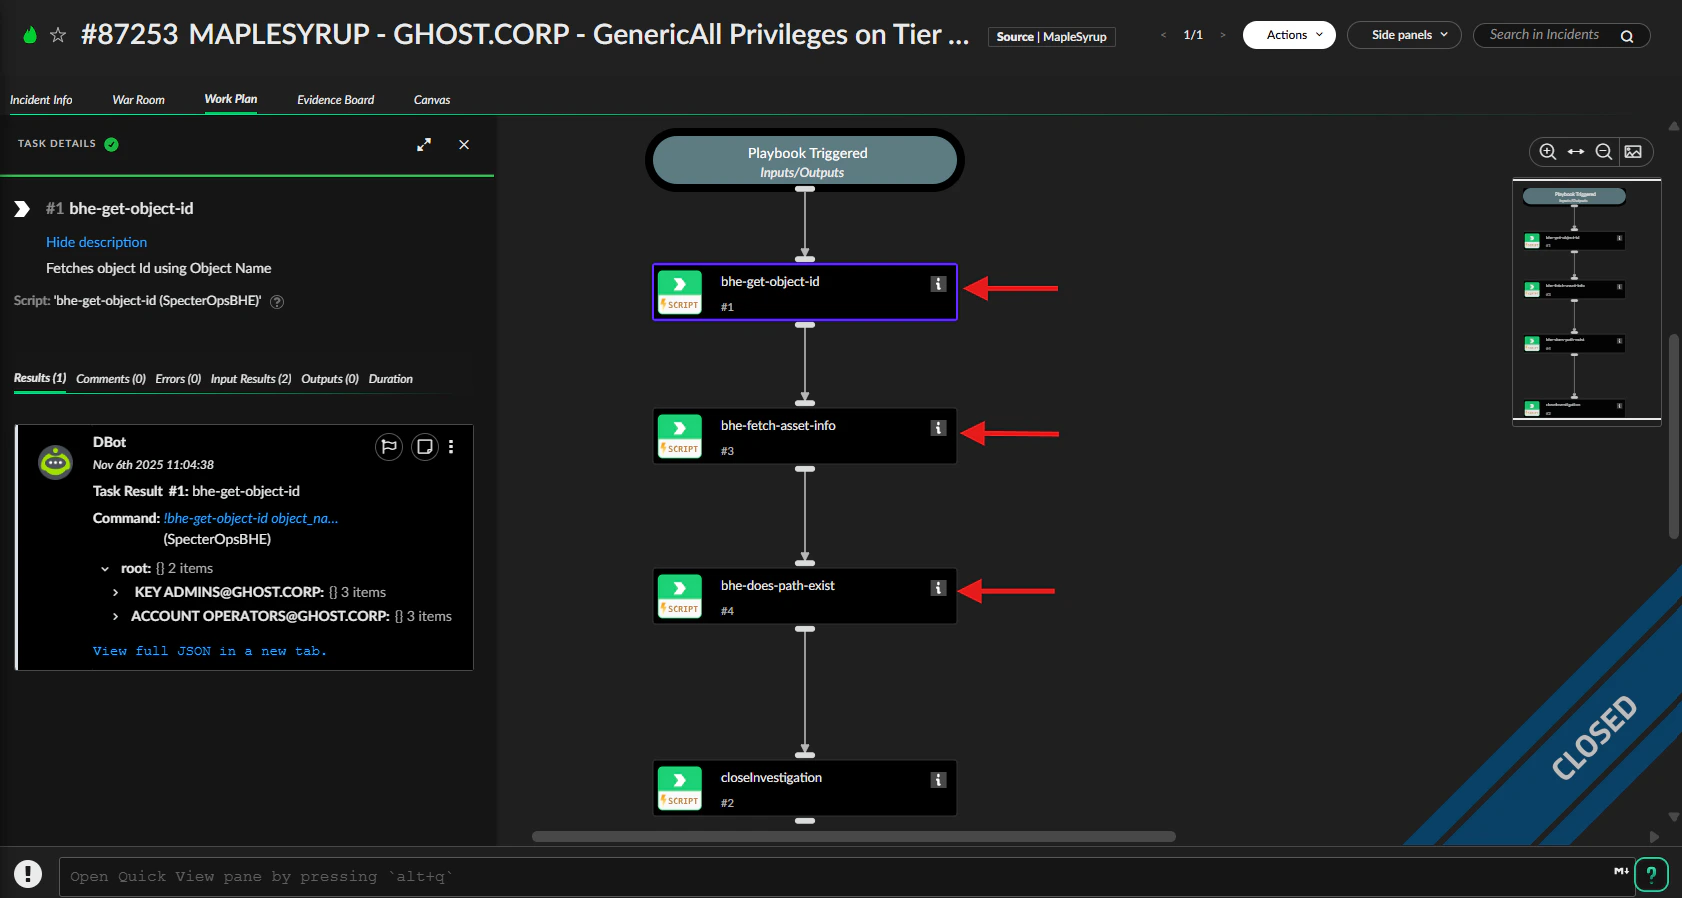
Click the Work Plan tab to view the playbook. The SpecterOpsBHE playbook runs custom commands to retrieve object-related information and analyze attack paths. You can click each task or script to view its results.
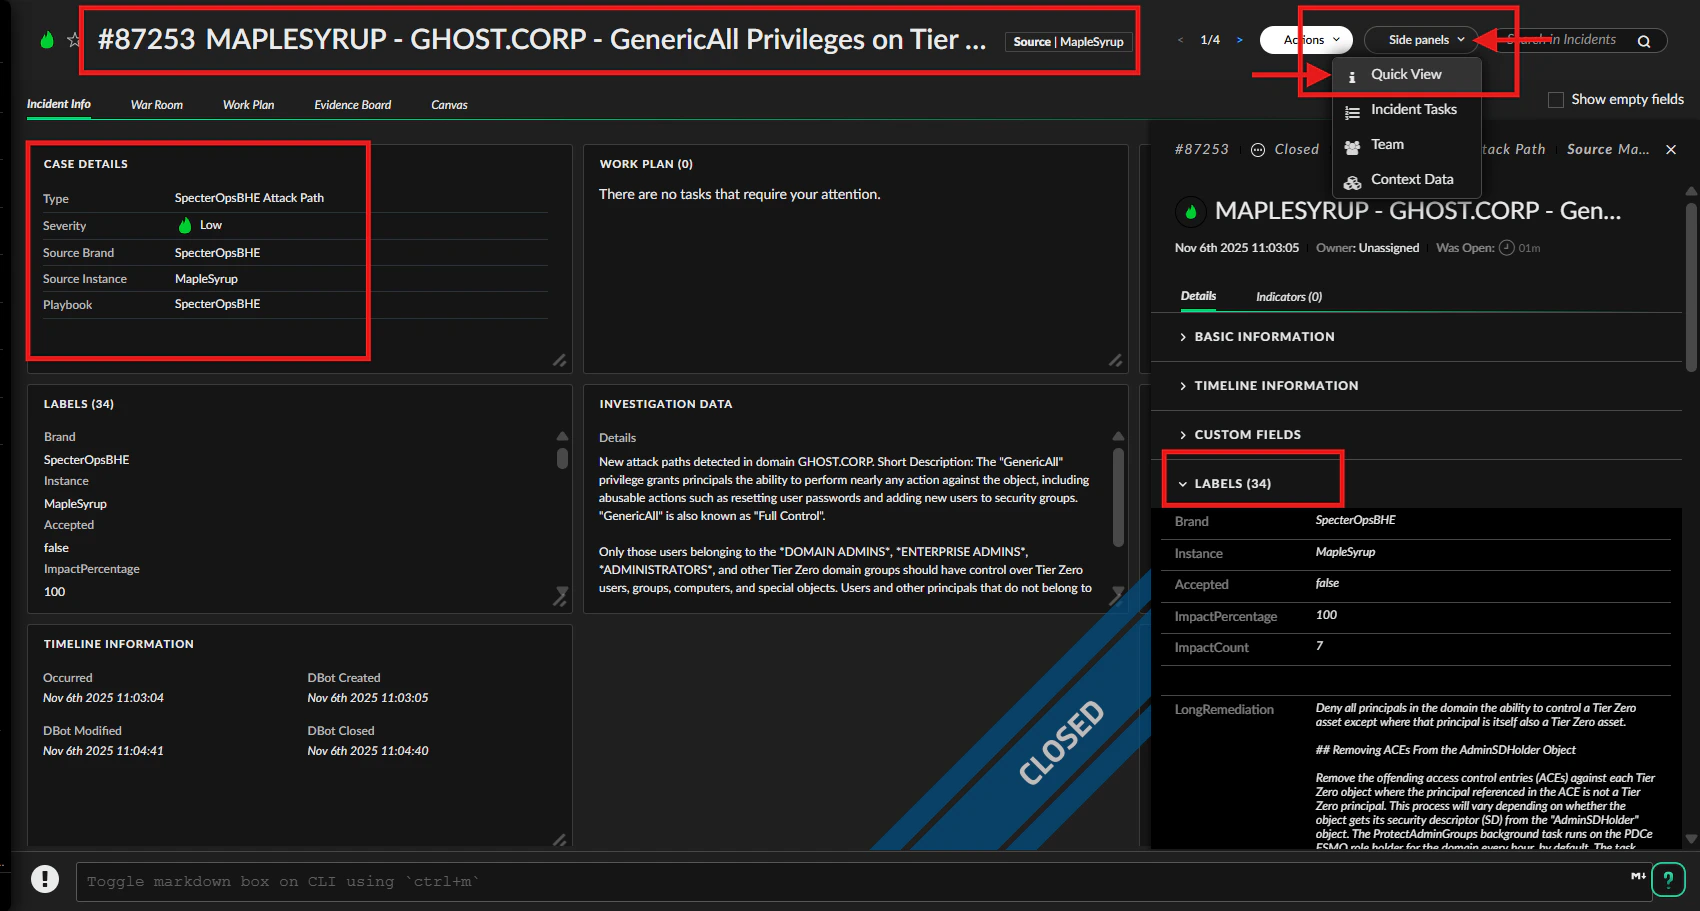
Use the DBot panel to review execution context and results. Locate the root section and expand it to see underlying data and command outputs related to the incident.


 After you configure the integration, Cortex XSOAR begins fetching BloodHound Enterprise attack path findings as incidents. Use the sections below to monitor ingestion, view incidents, and inspect details.