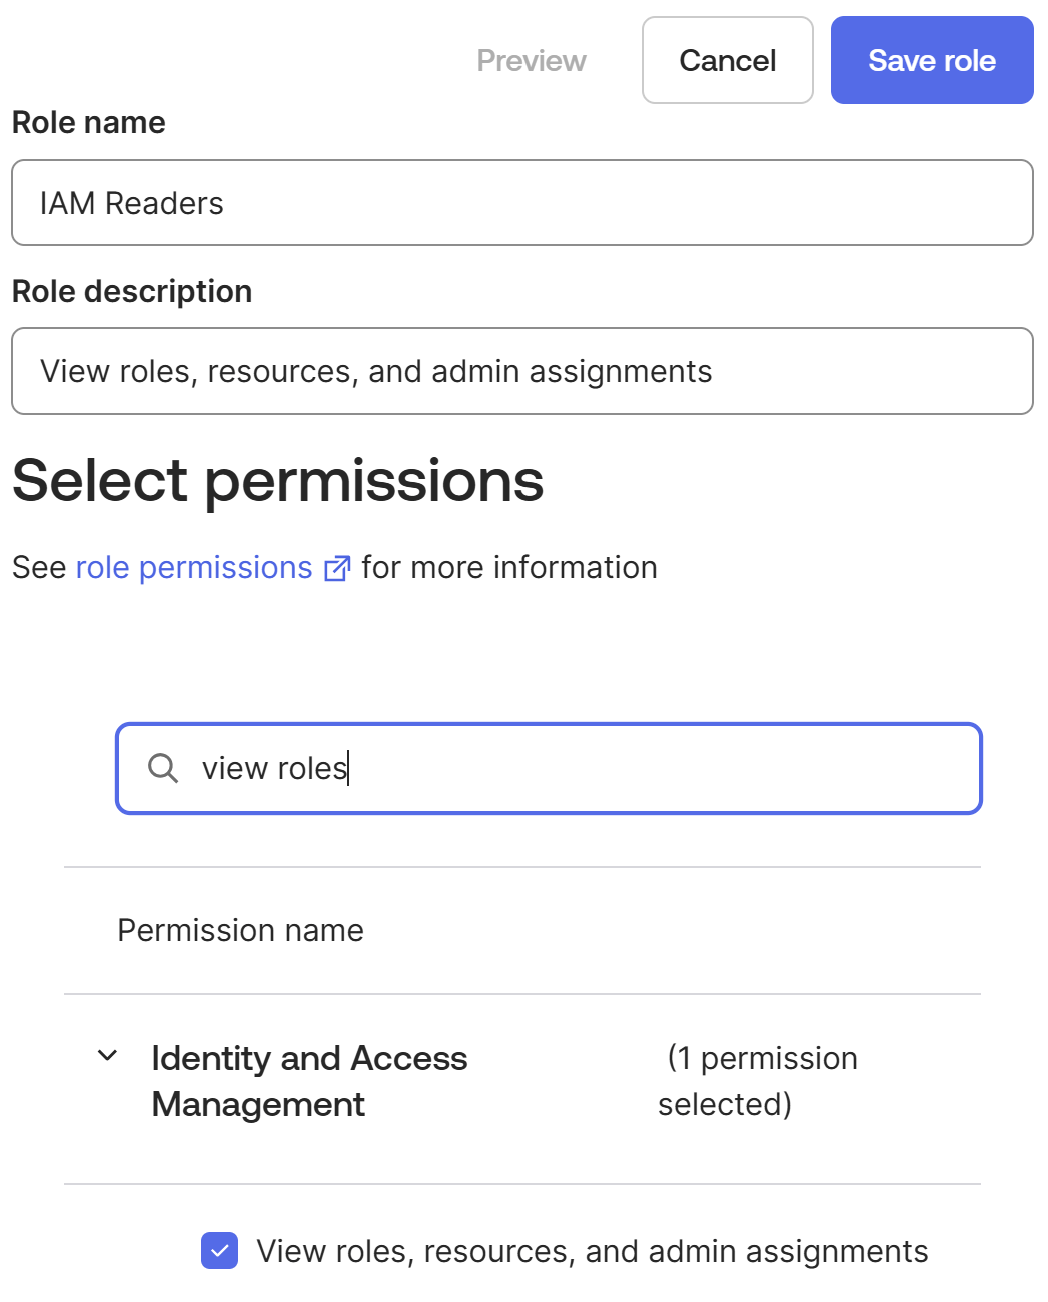
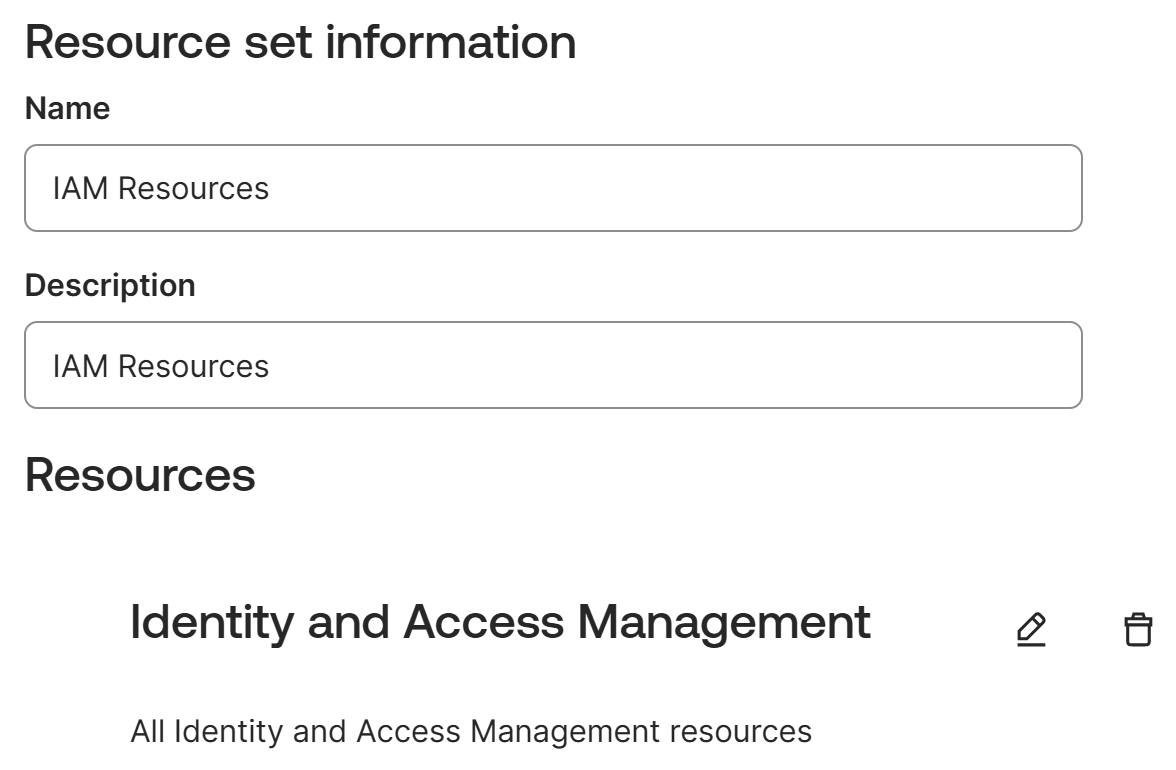
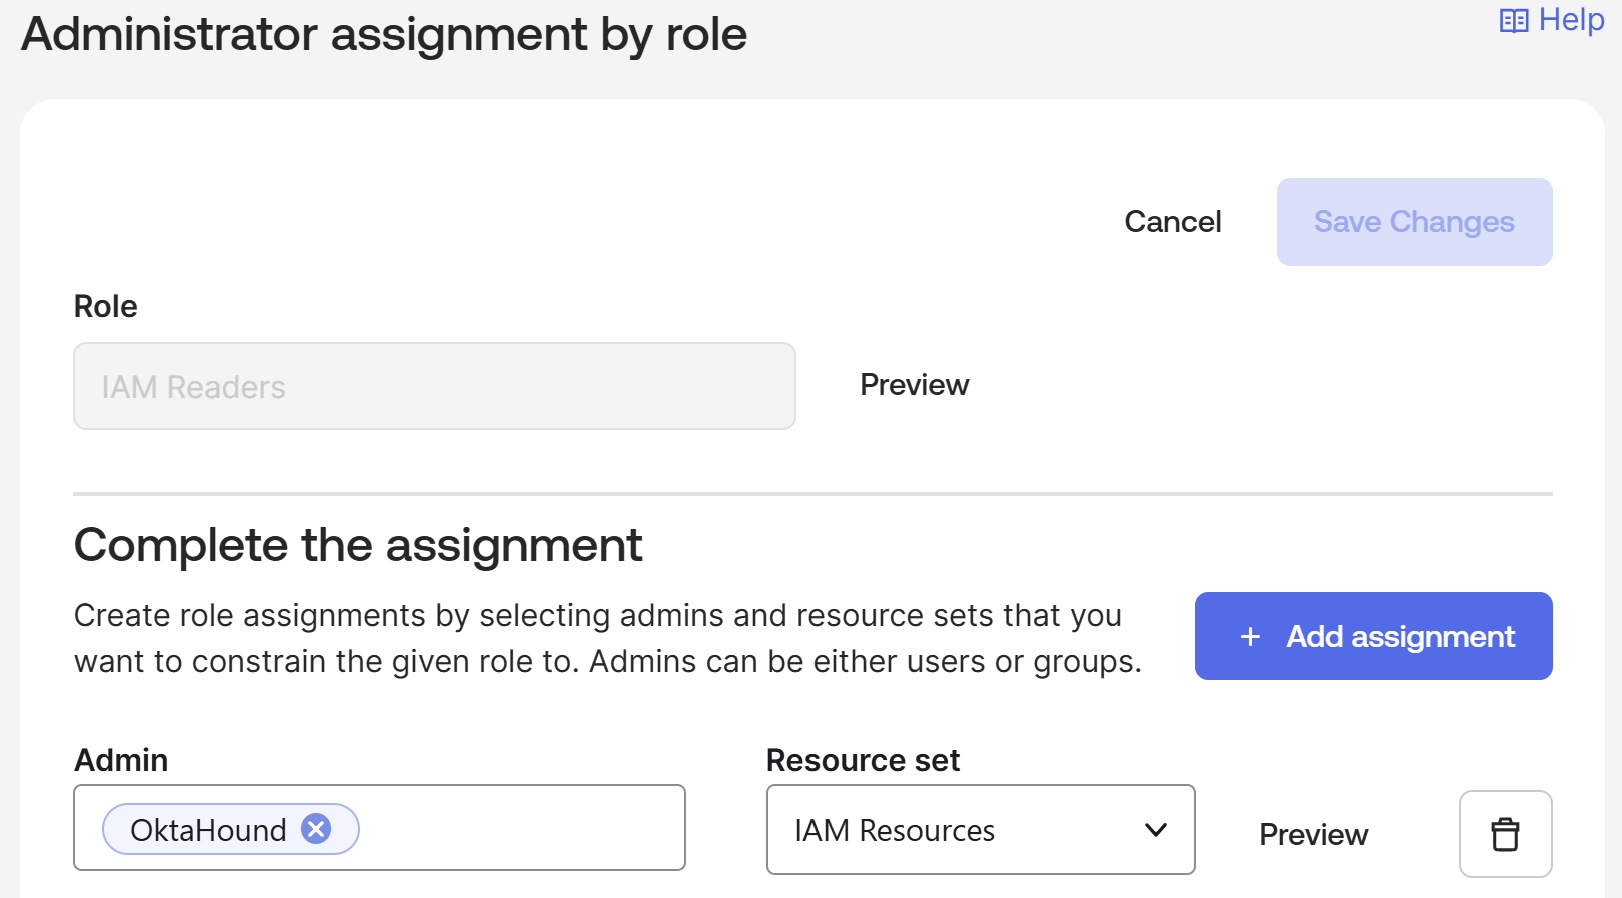
The OpenHound Okta collector authenticates to the Okta API using an OAuth 2.0 service application with a public/private key pair.
To create the Okta application registration for the OpenHound Okta collector, follow the steps below.
1
Open the Applications page
In the Okta Admin Console, navigate to Applications > Applications and click Create App Integration.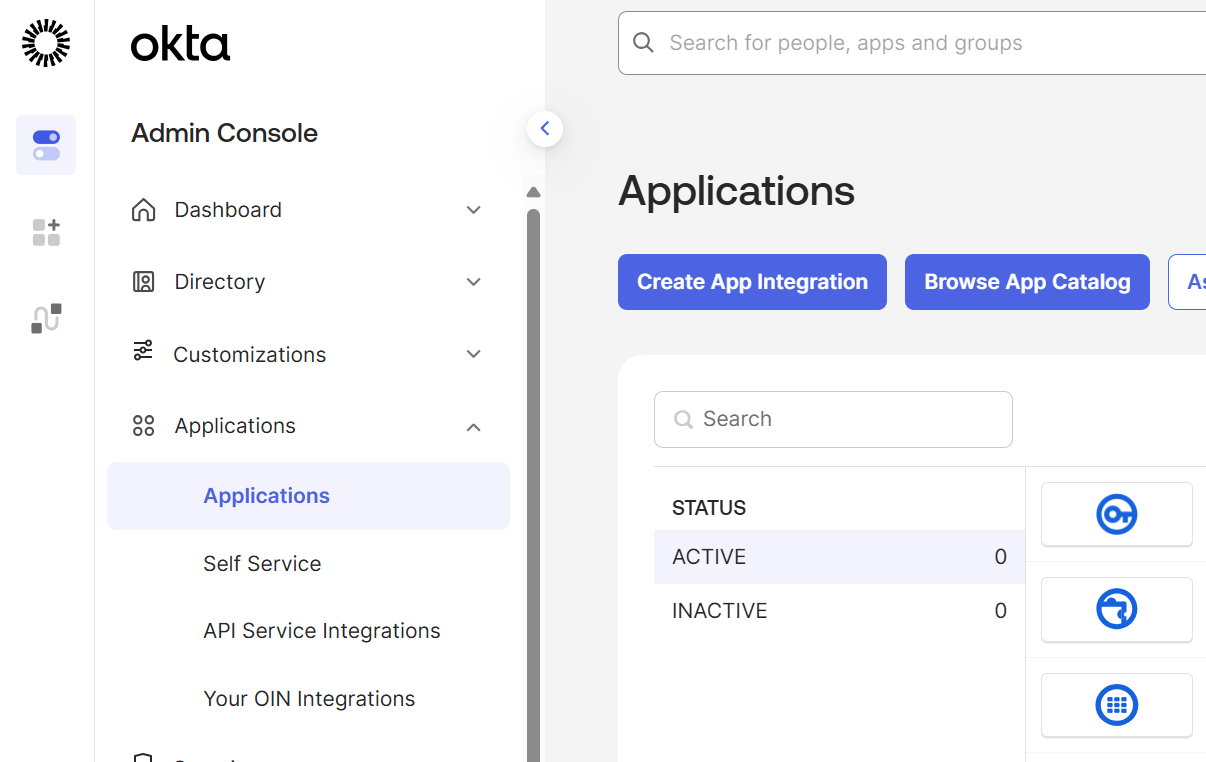
2
Select API Services
In the Create a new app integration dialog, select API Services and click Next.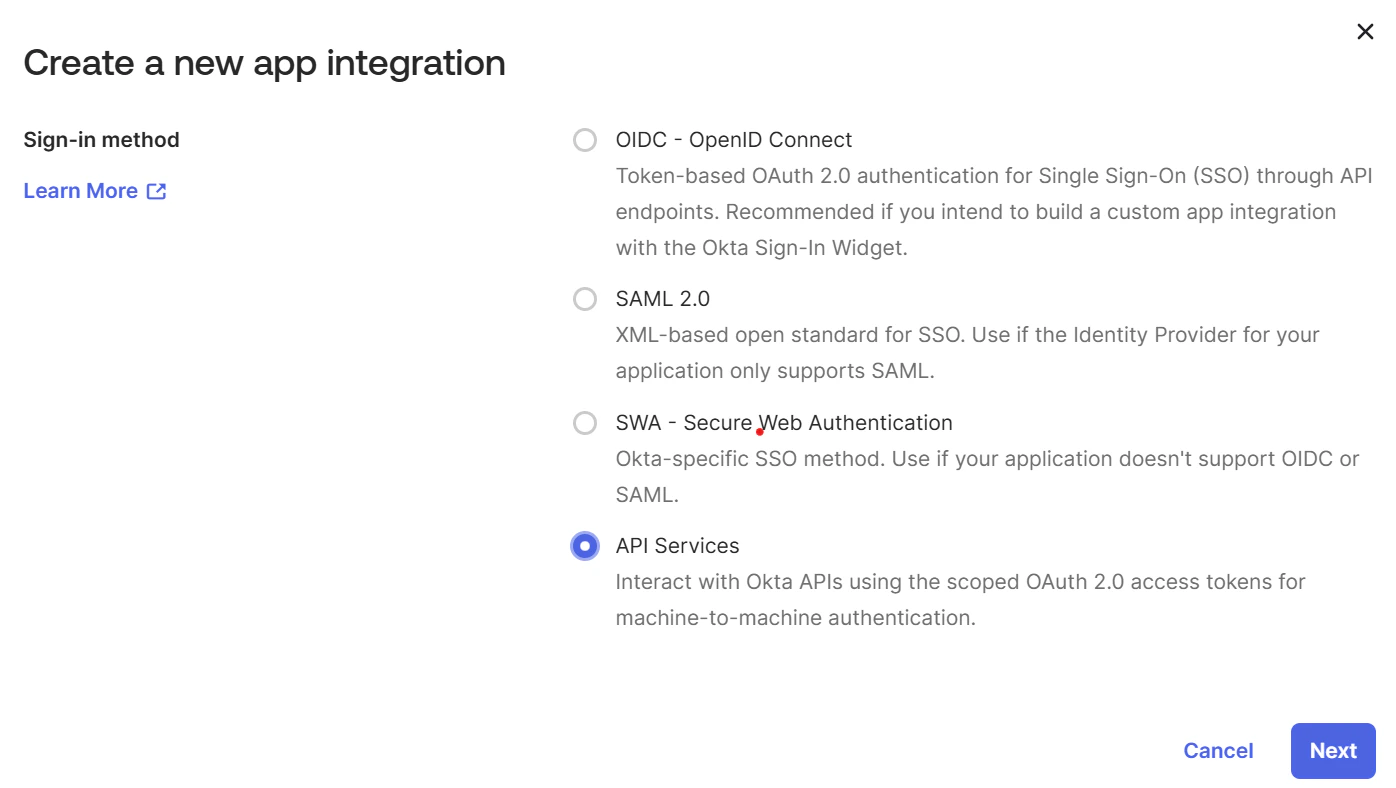
3
Name the application
Enter a name for the app integration and click Save.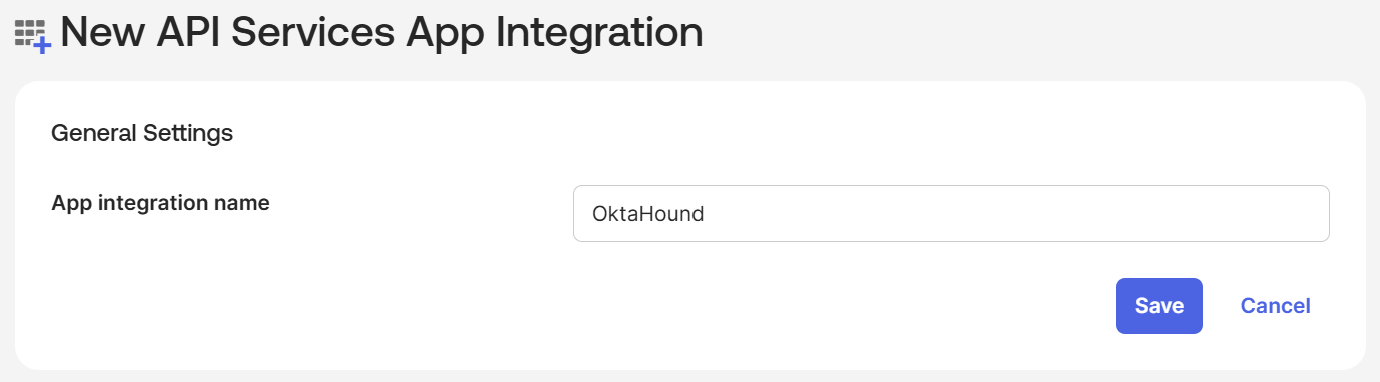
4
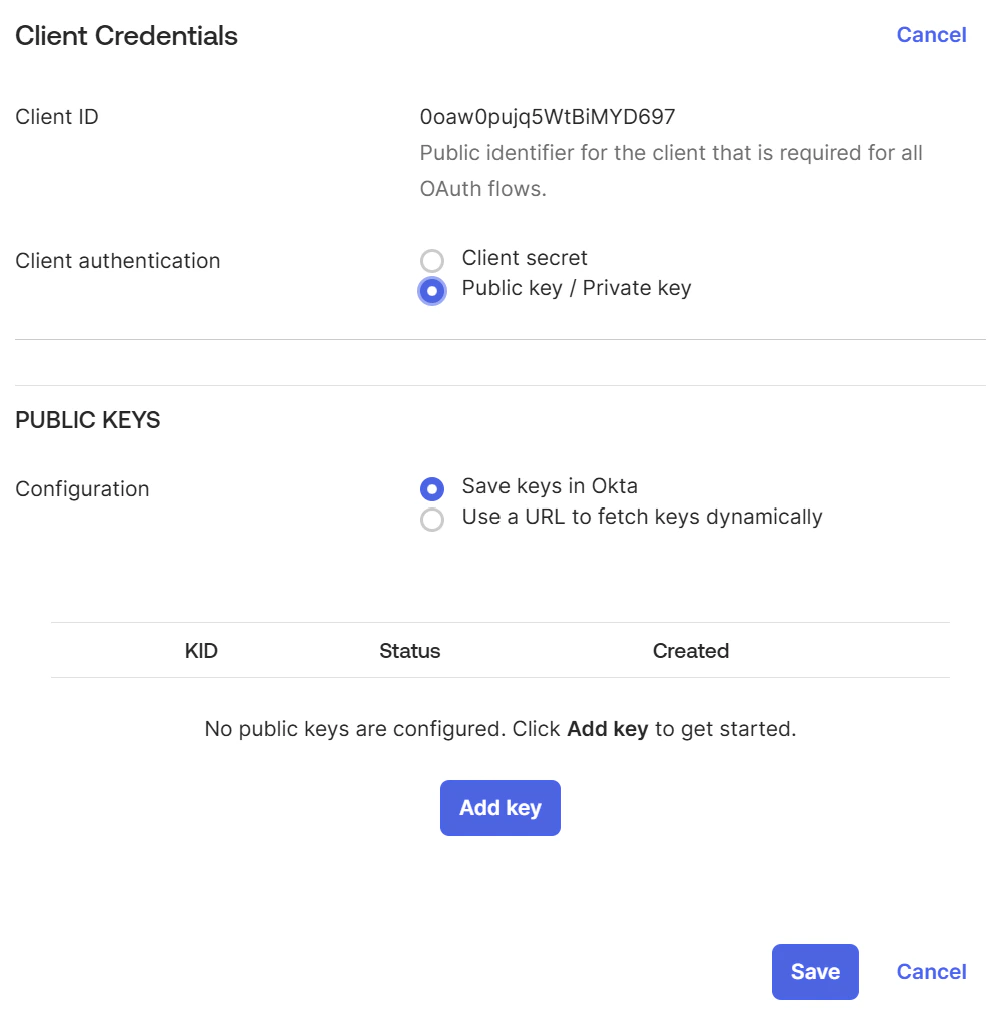
Configure public key authentication
After the application is created, you are taken to the General tab. Make a note of the newly created application’s Client ID for the collector.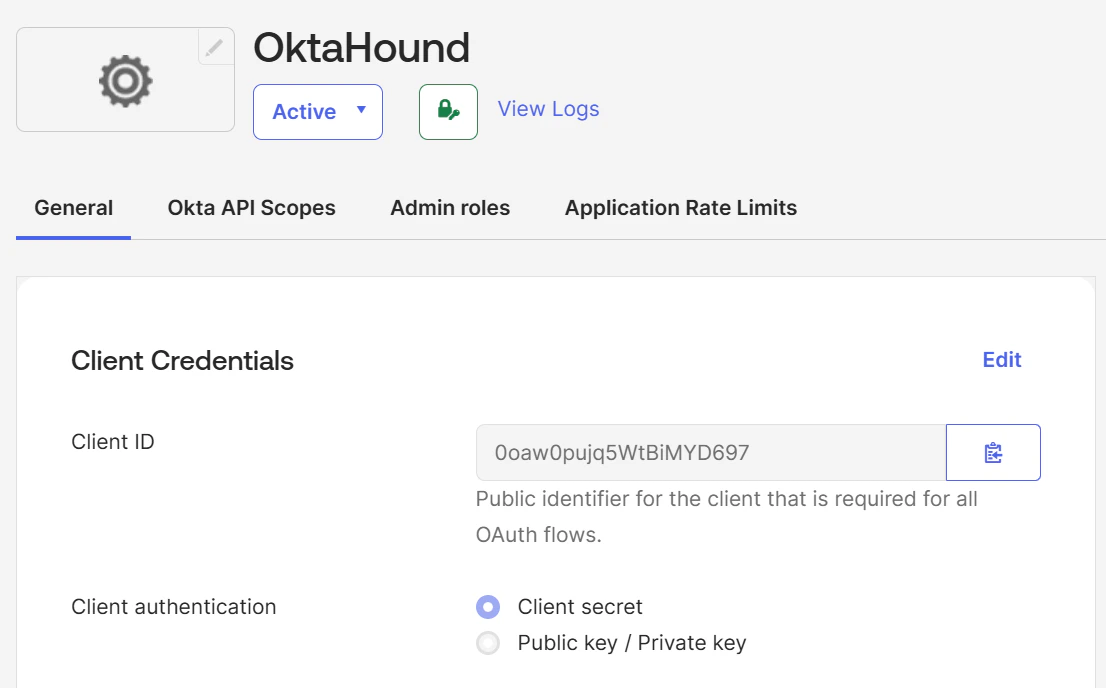
5
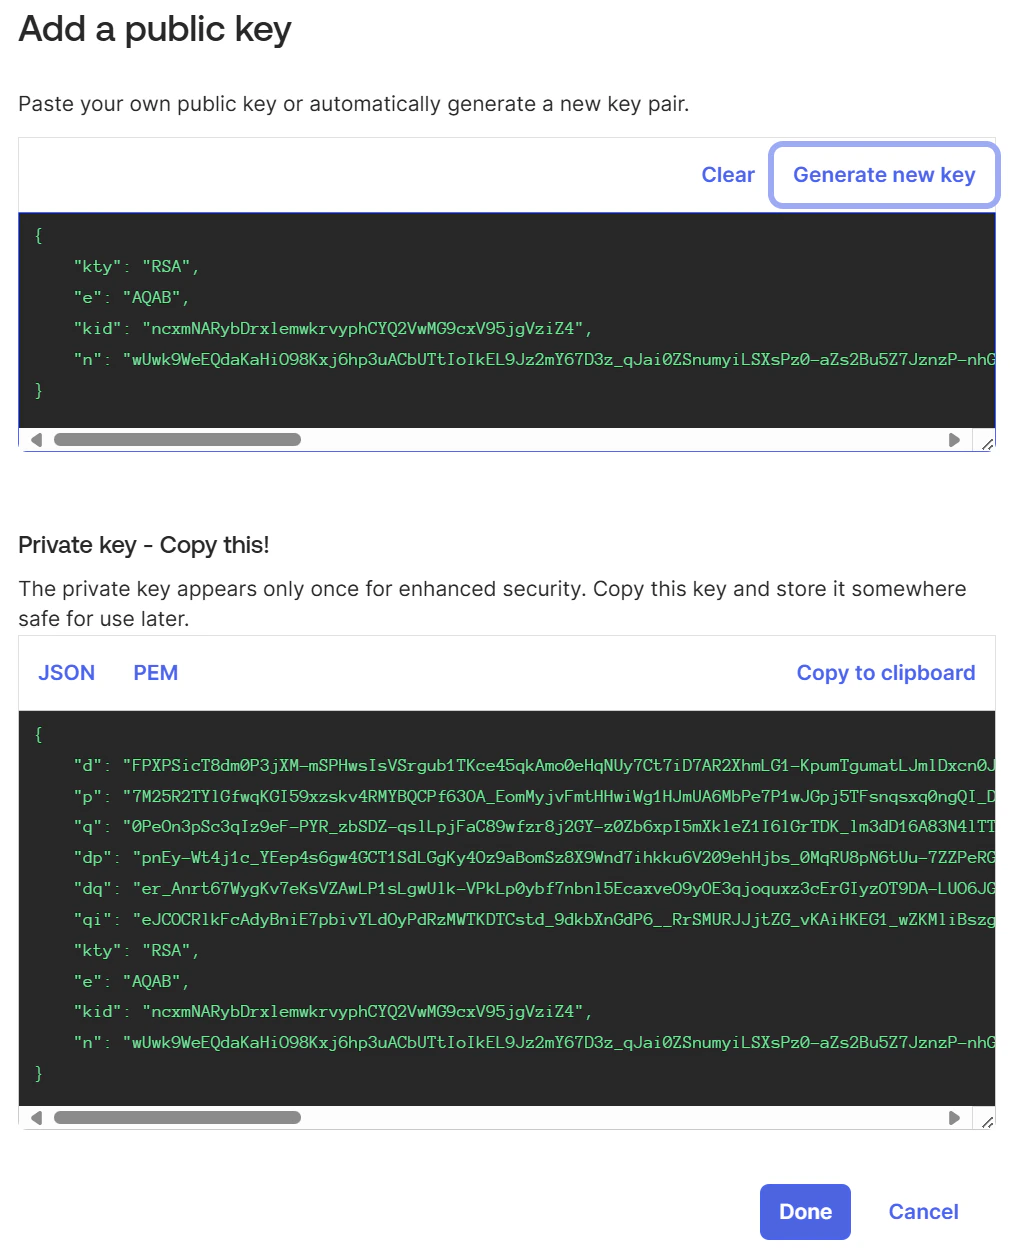
Generate a key pair
Under PUBLIC KEYS, click Add key, then click Generate new key.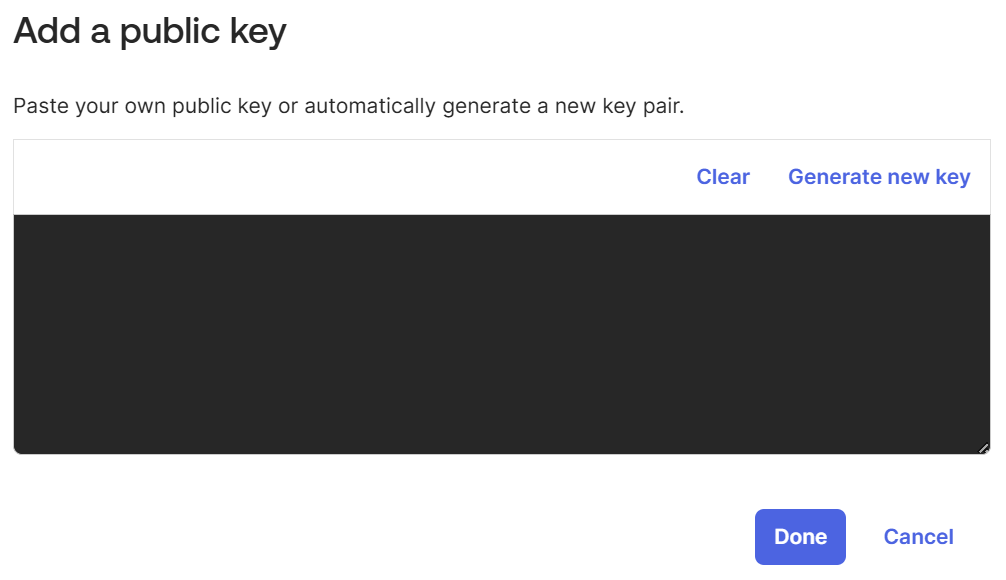
6
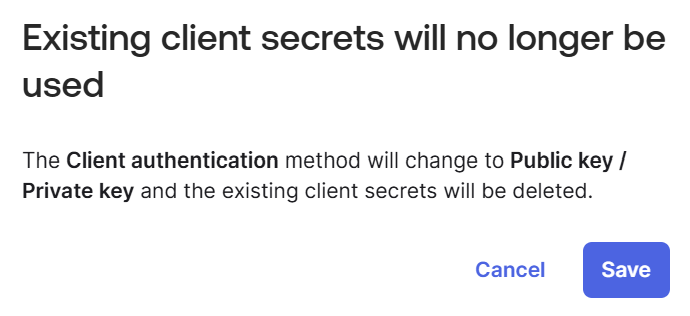
Save the credentials
Verify the key appears in the PUBLIC KEYS table, then click Save.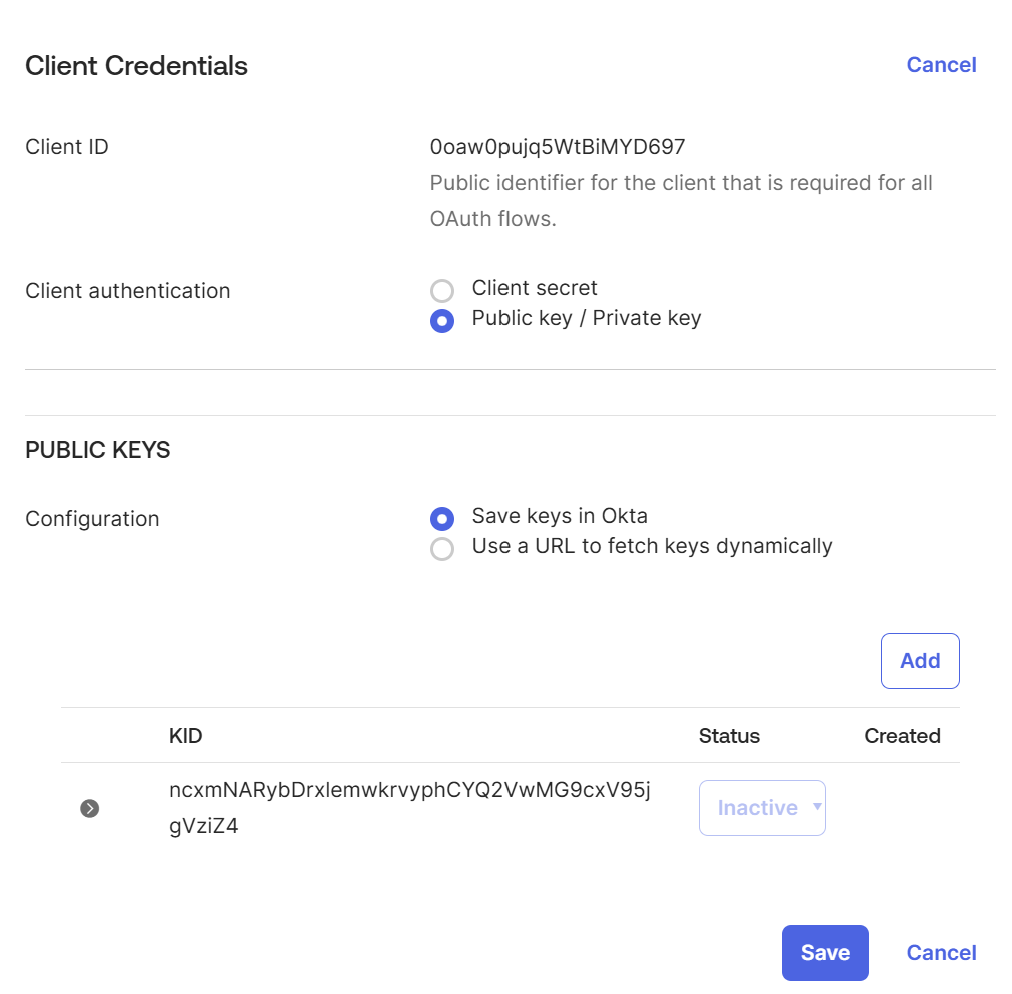
7
Disable DPoP requirement
Uncheck the Require Demonstrating of Proof of Possession (DPoP) option and click Save.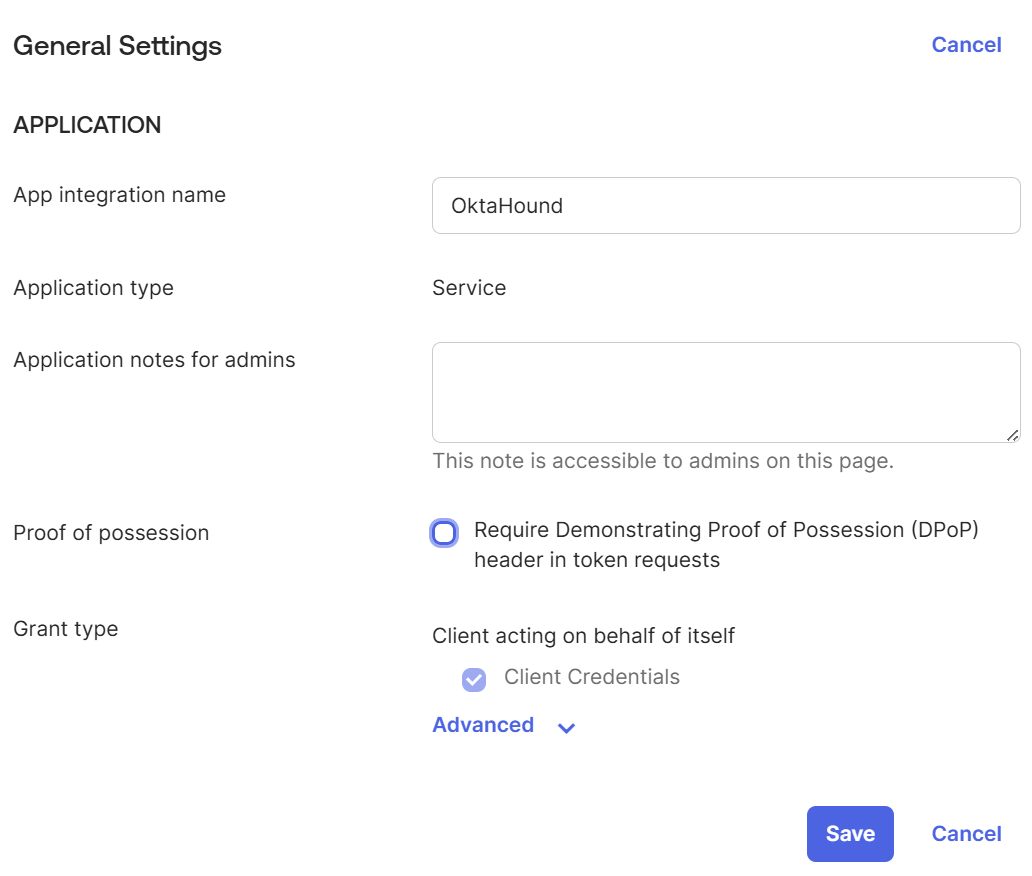
8
Grant OAuth 2.0 scopes
Navigate to the Okta API Scopes tab and grant the scopes required by the OpenHound Okta collector.The Okta application registration used by the OpenHound Okta collector requires the following OAuth 2.0 scopes for data collection to function correctly:
The
okta.realms.read and okta.realmAssignments.read scopes are optional and requires Okta Identity Governance or Secure Partner Access.9
Assign admin roles
In addition to the OAuth 2.0 scopes granted above, the application must also be assigned Okta admin roles.
Navigate to the Admin roles tab and assign one of the following role combinations:
- Full data collection
- Least privilege
Assign the Super Administrator role to the application.
The Super Administrator role is currently the only Okta admin role that allows reading application OAuth 2.0 grants and API service integrations,
as the permissions corresponding to the
okta.appGrants.read and okta.oauthIntegrations.read scopes cannot be delegated to custom admin roles.
Assigning the Super Administrator role to the application does not pose a security risk,
because its effective permissions are limited by the read-only OAuth 2.0 scopes granted above,
so the OpenHound Okta collector cannot modify any data in the Okta organization.